Specialized Cyber Security Search

Expert-tuned relevance

4CyberSecurity is a focused search engine built for people who need precise, relevant results about Cyber Security. It aggregates multiple specialized indexes, expert-ranked signals, and AI-driven summaries so you can find CVE entries, vendor guidance, tools, research papers, and related services without sifting through general web noise. Part of the 4SEARCH network of topic specific search engines.

Uniswap V4 Security Guide: Hooks, Pools, and New Attack Vectors You Need to Know Before Deploying

Uniswap V4 hooks are the most powerful — and most dangerous — primitive in AMM history. One malicious or misconfigured hook can drain an entire pool in a single transaction. Here's what every developer and DeFi user needs to check before touching V4. I've gone through the V4 architecture, the PoolManager contract, and a stack of early hook implementations. What I found surprised even me — and I audit contracts for a living. The vulnerability surface here isn't just new, it's fundamentally different from anything that came before in AMM design. Let me walk you through exactly what's at risk. Uniswap V4 moves all pools into a single singleton contract called PoolManager. Instead of deploying a new pair contract for every token pair (V2/V3 style), every pool lives in one contract and is identified by a PoolKey struct. This reduces gas significantly — but it also means a bug in one pool's…

1,128 words2 outlets

Oracle Security Alert Advisory - CVE-2026-114820

Security vulnerabilities addressed by this Security Alert affect the products listed below. Please click on the links in the Patch Availability Document column below to access the documentation for patch availability information…

364 words2 outlets
More in Vulnerabilities

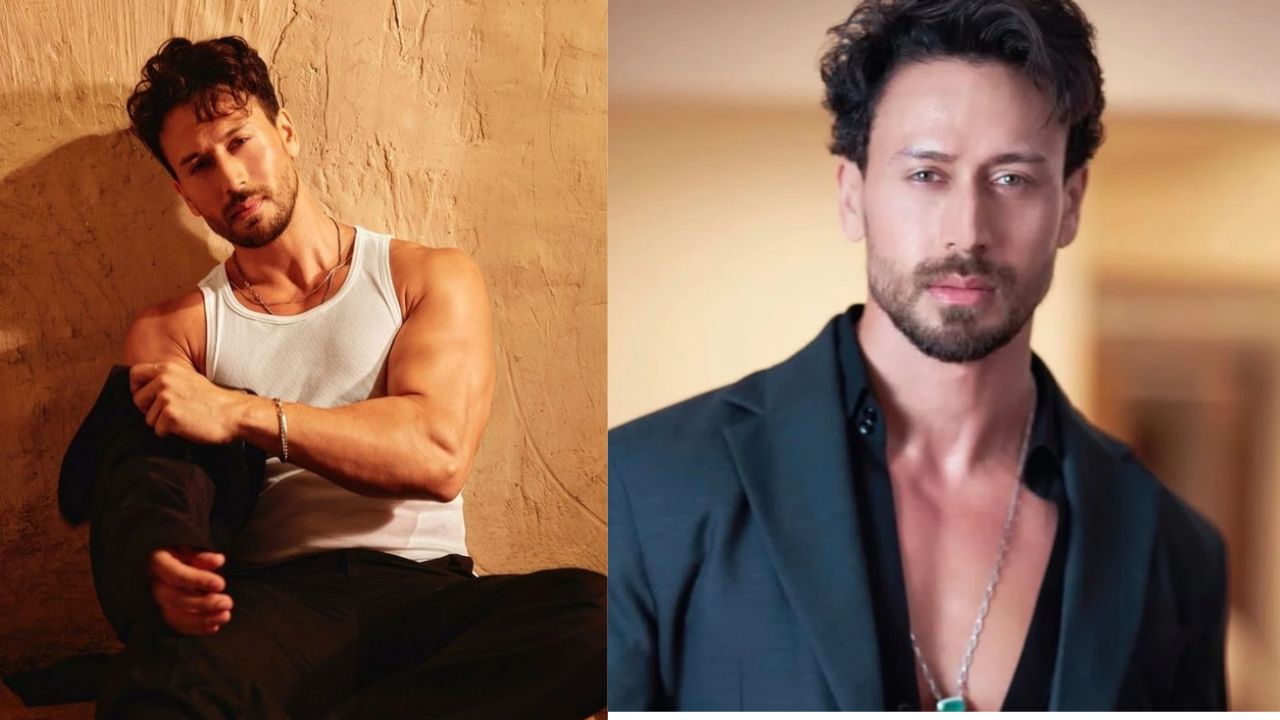
Tiger Shroff firing case: Shooters received real-time updates from handler, monitored TV news

Home » General » Environment » Tiger Shroff firing case: Shooters received real-time updates from handler, monitored TV news Posted By: Gopi October 23, 2026 Mumbai, Oct 24 (SocialNews.XYZ) The investigation into the firing incident targeting Bollywood actor Tiger Shroff has revealed that the shooters were in constant contact with their handler through phone calls and messages. Investigators suspect that the accused were also receiving real-time updates about the police investigation, including information broadcast on television news channels. According to sources, the shooters remained in touch with their handler during and after the October 18 attack. They were provided with updates about developments in the case and the police operation to identify and apprehend them. Sources said that after information about the shooters' identities and appearances began emerging, the handler…

609 words3 outlets
More in Ransomware

Rotifer v0.9.1: Content-derived gene IDs for the LAN P2P node (npm 0.27.0)

v0.9.1 changes what a gene's ID is. It is no longer a name someone typed; it is v2: followed by a SHA-256 computed from the gene's contract and code. The P2P announcement that carries that ID now has a frozen wire format, and every announcement is validated before a node forwards it. We checked it the way a user would: two real machines on one Wi-Fi, both installed from npm at 0.27.0. An announcement made on one appeared on the other within 1.36 seconds, with the same gene ID on both ends. v0.9.1 is the protocol version; the npm package that ships it is @rotifer/playground v0.27.0, available now. Until now, a P2P announcement identified a gene by a string the publisher supplied, in practice its name. Any node could announce hello-world, and any node could announce a different gene under the same name. A name is a label the publisher claims. It tells a receiver nothing about what the…

911 words

Send crypto in Trezor Suite

Sending crypto in Trezor Suite works the same way for almost every asset: pick the account you're sending from, enter the recipient's address and the amount, then check the details on your Trezor and sign. This guide covers the…

951 words
More in Malware and Phishing

Privacy commissioner looking into Crime Stoppers tip line hack. Here’s what you need to know

The breach could render tipsters vulnerable to identity theft, fraud and in some cases risk their public safety, according to experts. A large-scale Crime Stoppers data breach exposed nearly 1.5 million Canadian tips, nearly 180,000 of which were submitted in Toronto. The federal privacy commissioner is examining a large-scale Crime Stoppers data breach that exposed nearly 1.5 million Canadian tips, prompting some local branches to pause the program amid security and safety concerns for tipsters. Despite the breach falling outside their mandate, Vito Pilieci, spokesperson for the Office of the Privacy Commissioner of Canada, said the agency has offered “expertise and guidance” in the aftermath of the breach, and is seeking more information from Navigate360 “before determining next steps.” Pilieci said he was not in a position to comment further. As first reported by CBC, the information…

822 words2 outlets
More in Hackers and Threats